Technical Advisory
CitrixBleed required a session response
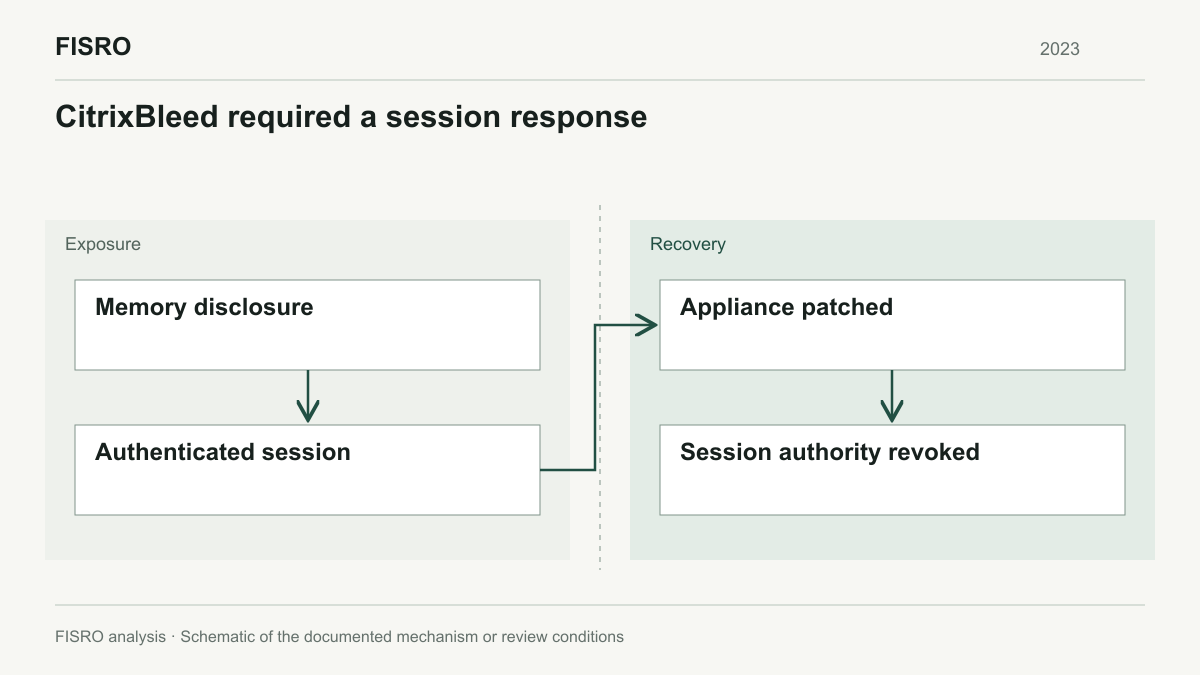
CVE-2023-4966 linked a memory-disclosure flaw to reusable sessions that needed a separate recovery decision.
Event / disclosure
Security cases, technical advisories and analysis. Browse the record by event date, subject or product.
24 publications. Browse by event date below, or use the incident archive for a year-by-year view. Publication dates appear on each article.
CVE-2023-4966 linked a memory-disclosure flaw to reusable sessions that needed a separate recovery decision.
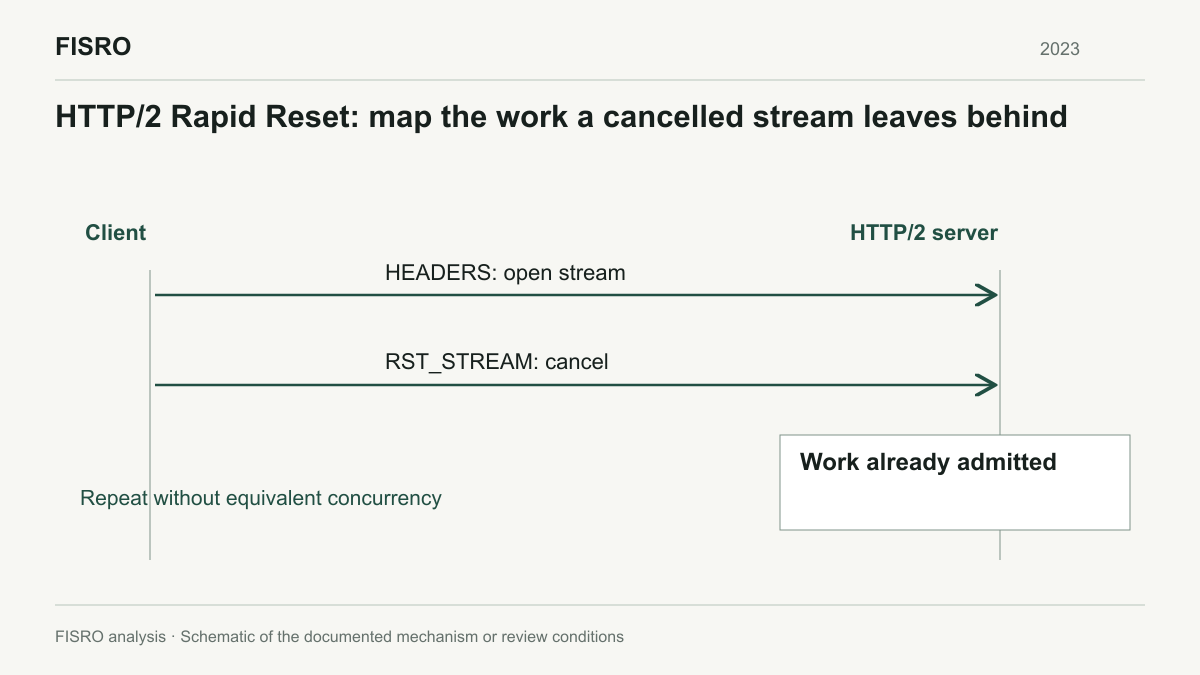
CVE-2023-44487 made request churn and protocol termination more useful questions than a connection count alone.
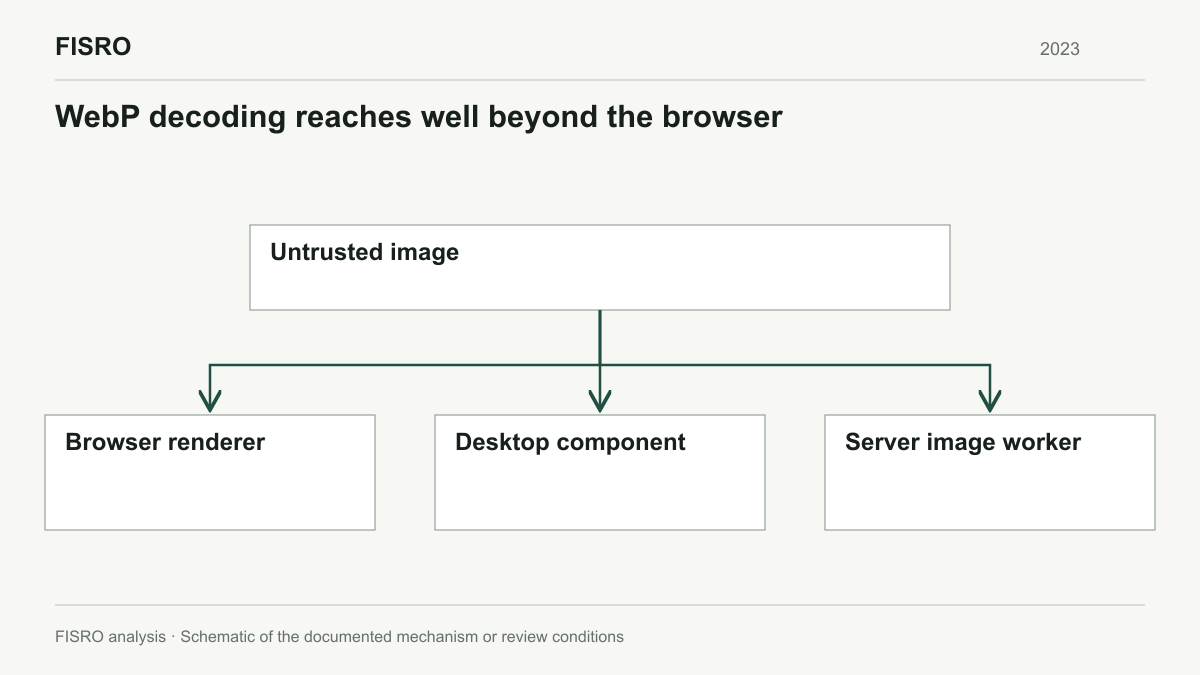
CVE-2023-4863 required inventory of browsers, embedded renderers and image-processing workers.
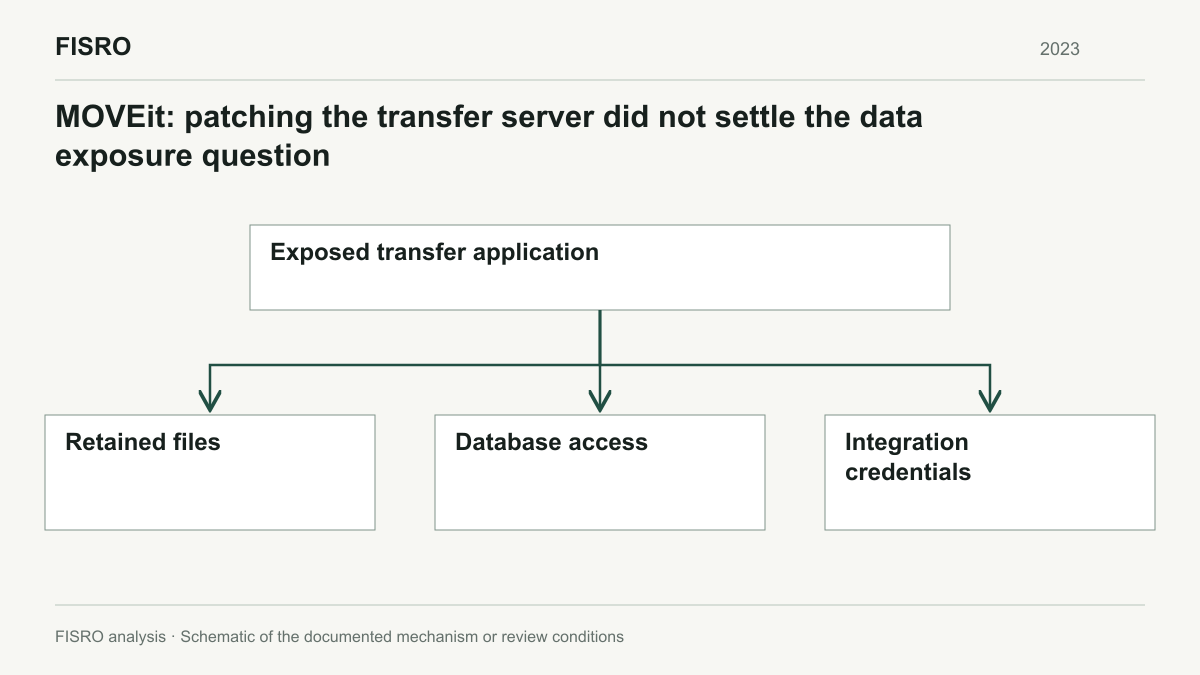
The 2023 campaign separated two jobs that incident tickets often collapse: closing the vulnerability and investigating earlier access.
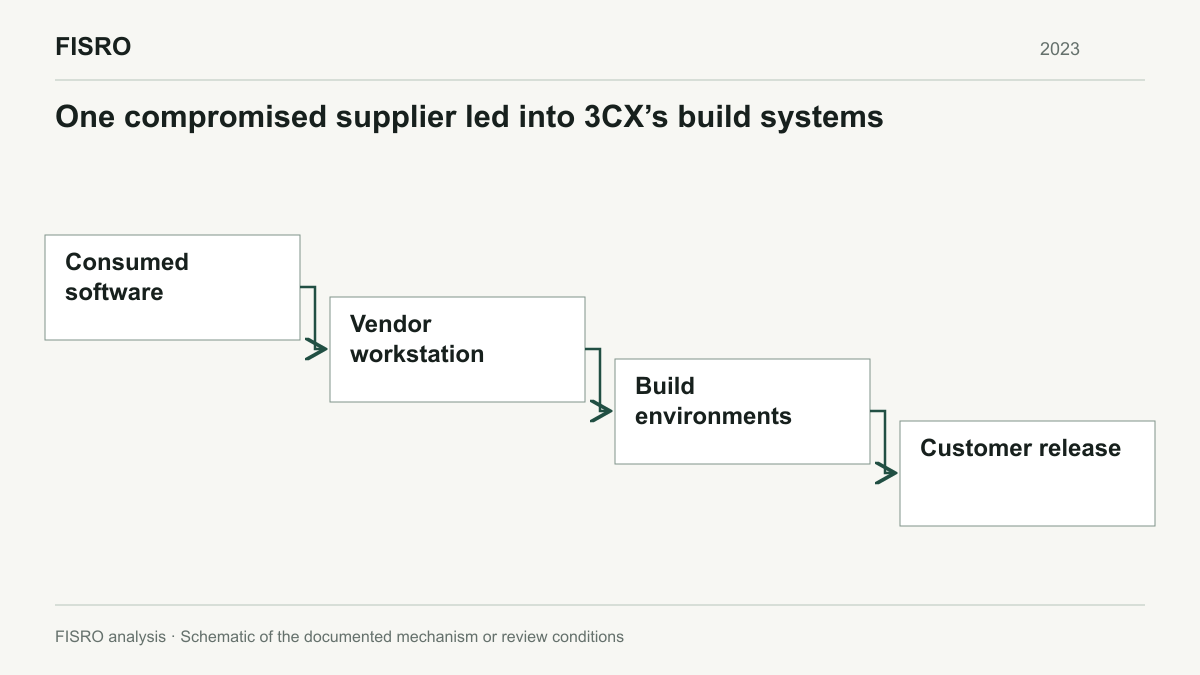
The 3CX investigation traced a compromised software input into another vendor’s release environment.
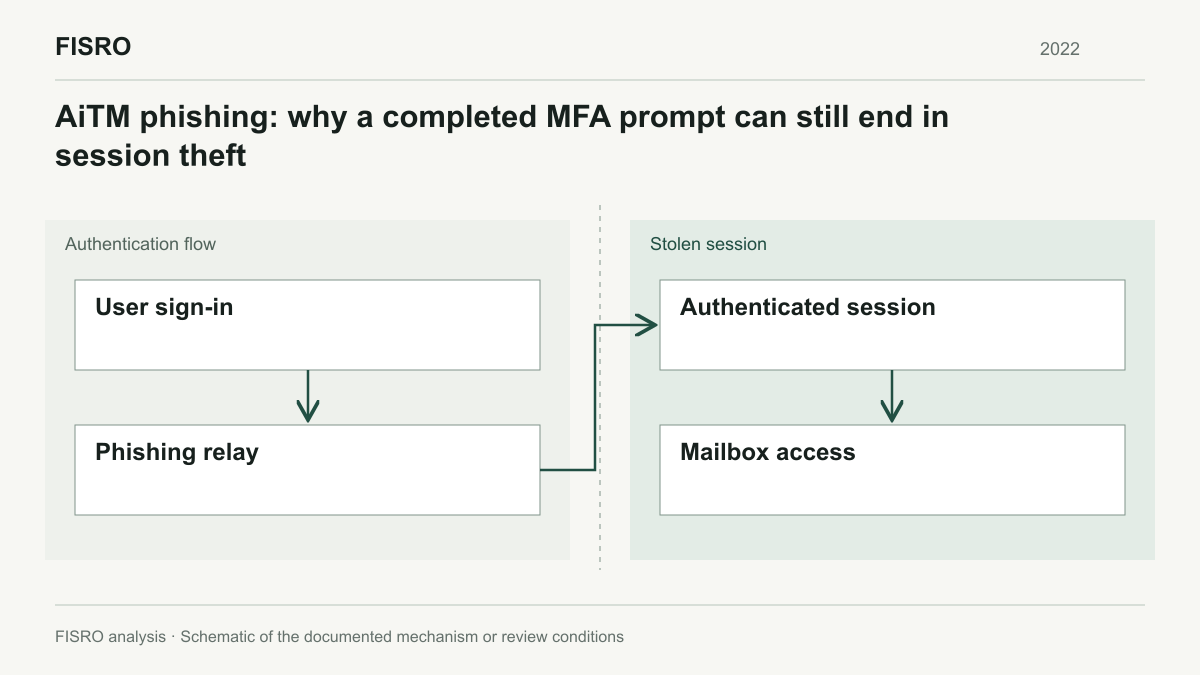
The recovery task follows the stolen session into the mailbox, its persistence settings and the business conversations it exposed.
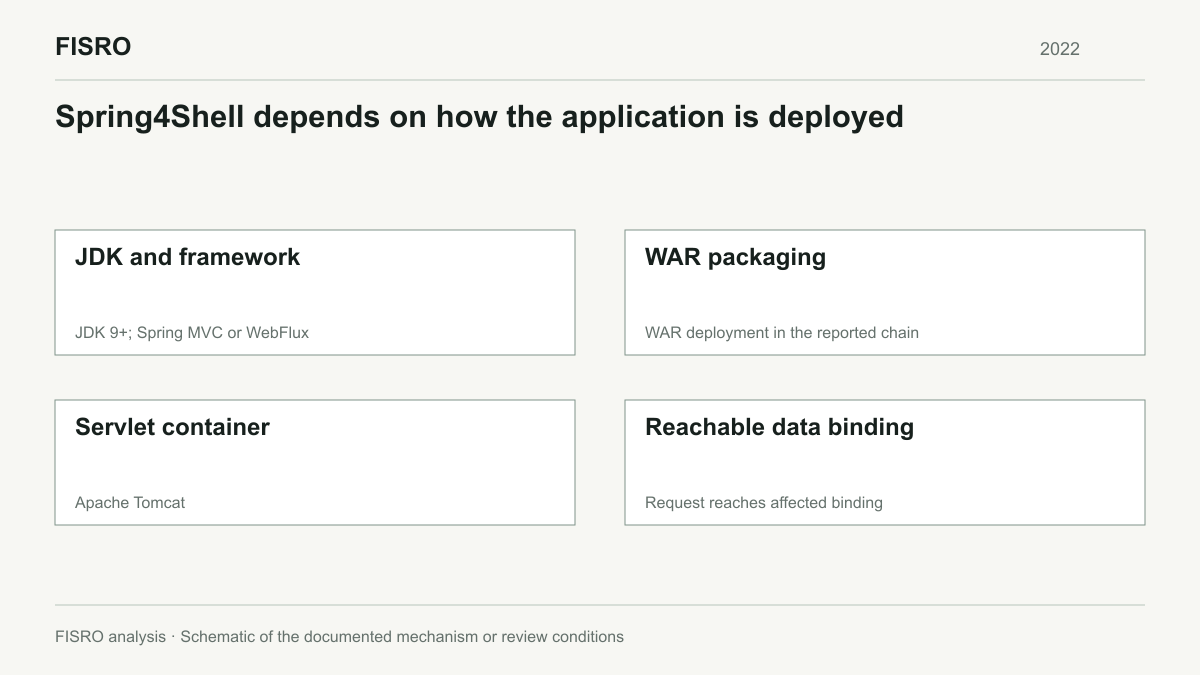
Assess CVE-2022-22965 using the actual runtime, Spring dependencies, packaging and servlet container.
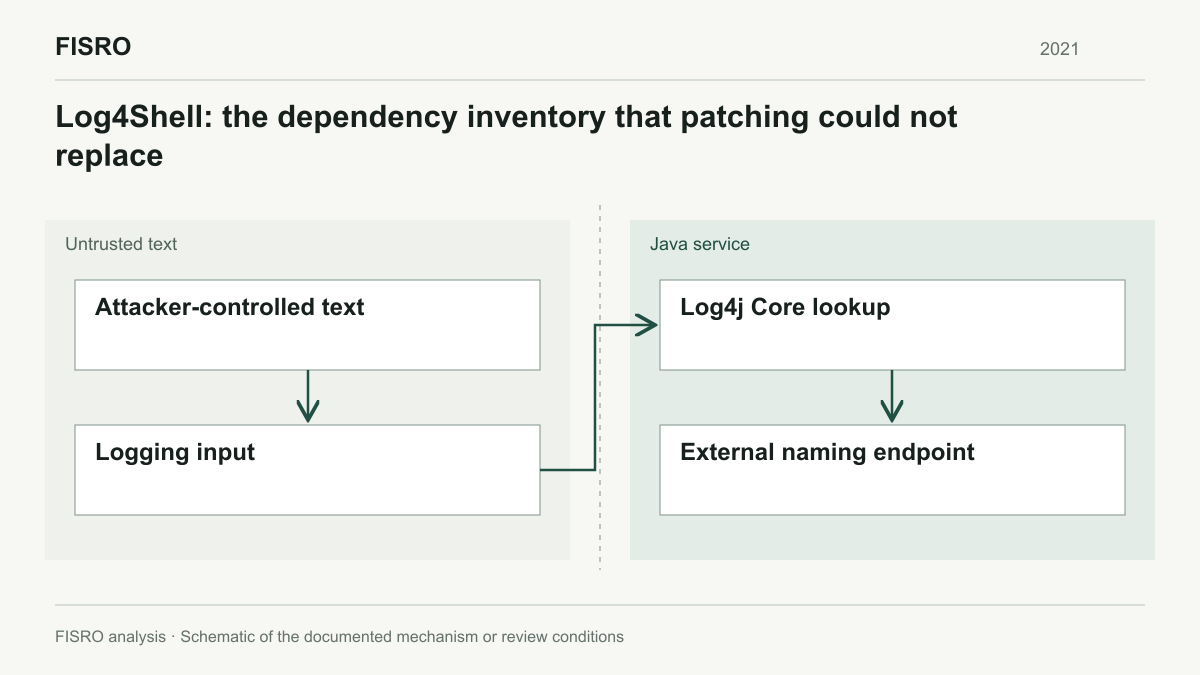
A retrospective on embedded Java dependencies, incomplete early fixes and the evidence needed to close a remediation ticket.
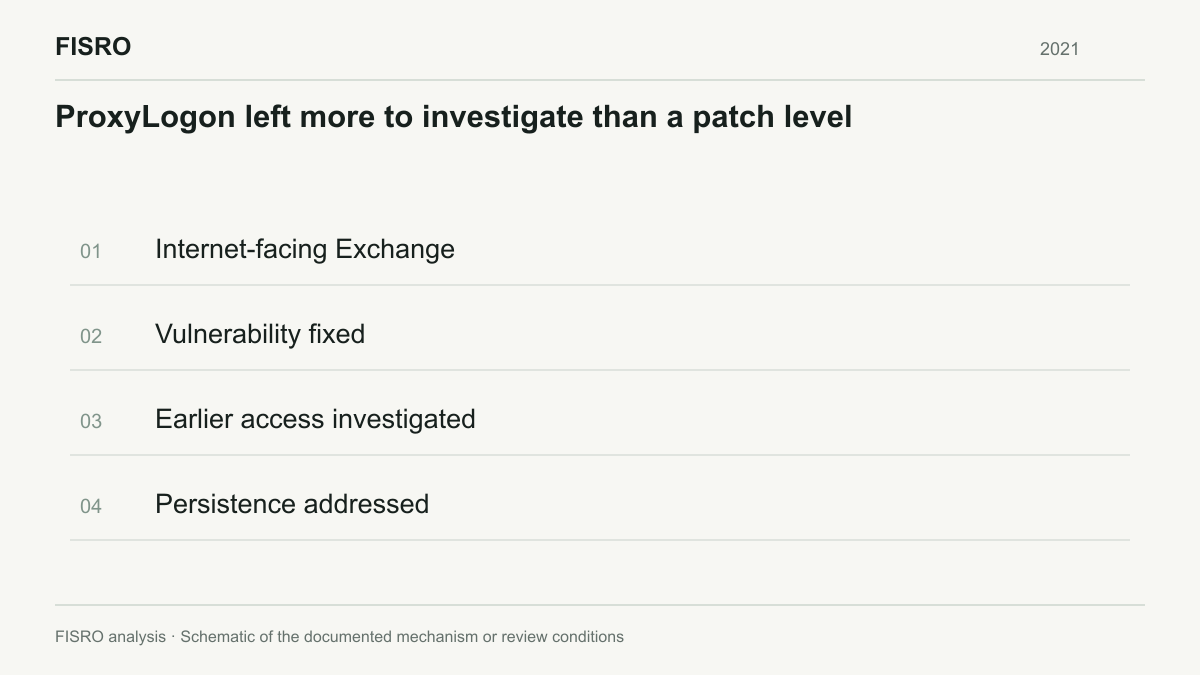
Exchange patch state, earlier exploitation and persistent access need separate evidence in a ProxyLogon response.
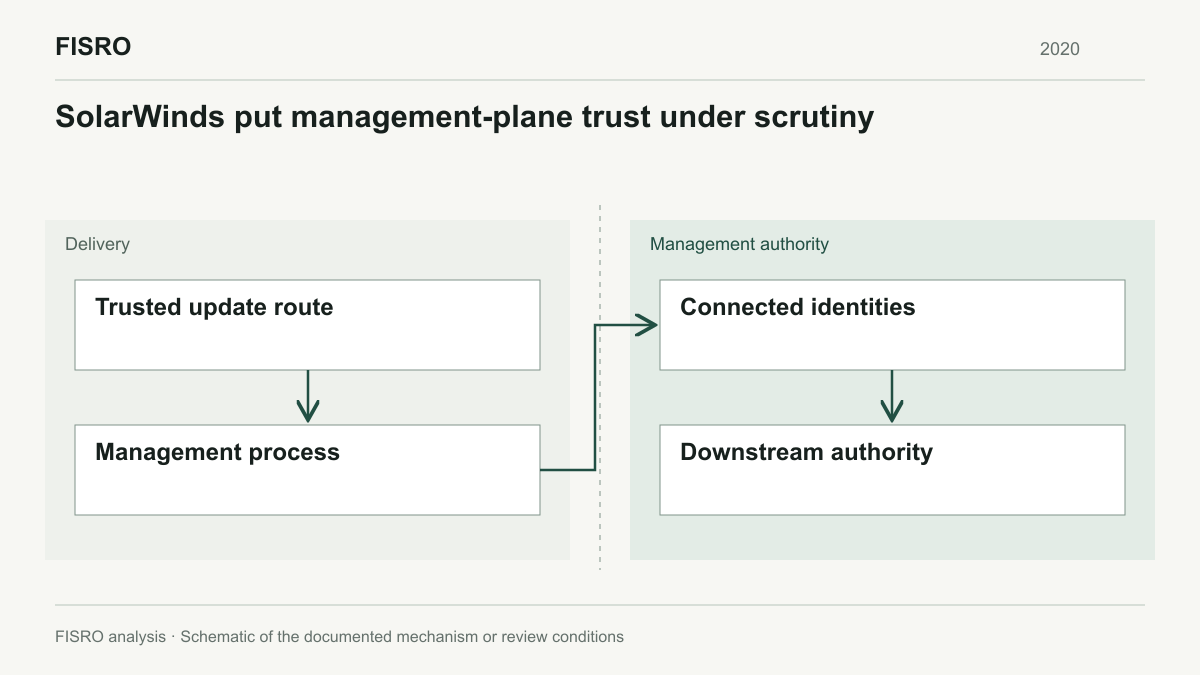
SUNBURST made software provenance, management identities and independent recovery part of the same investigation.
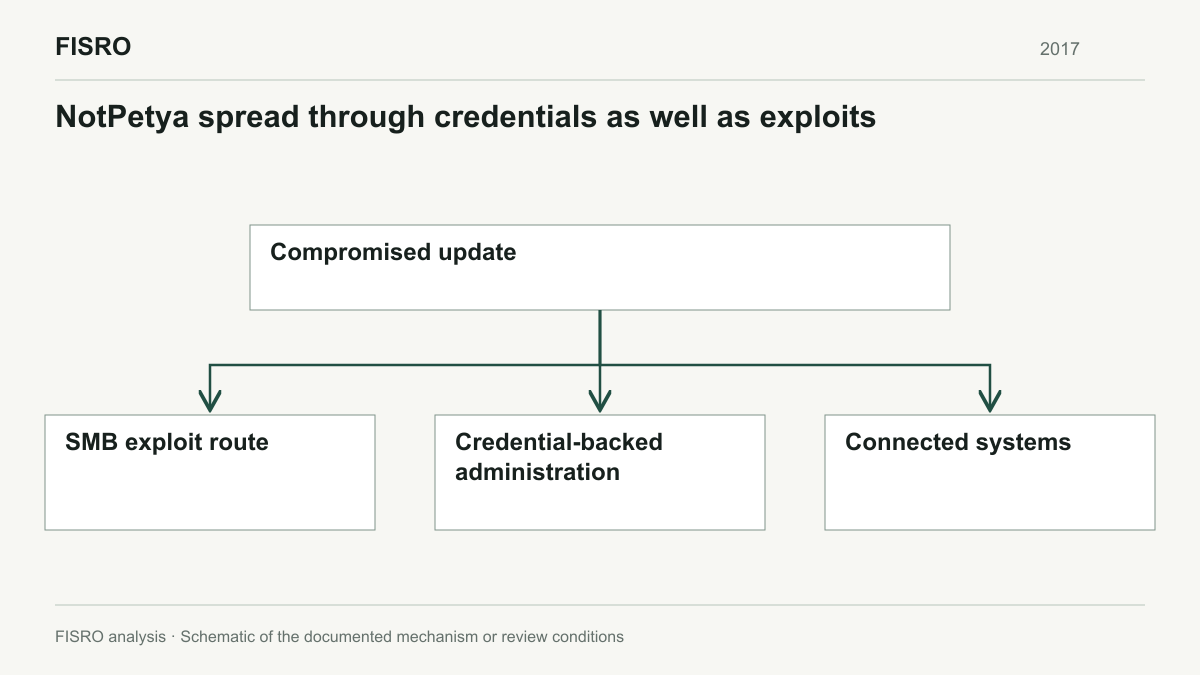
The NotPetya record connects a poisoned update, stolen credentials and remote administration across recovery boundaries.
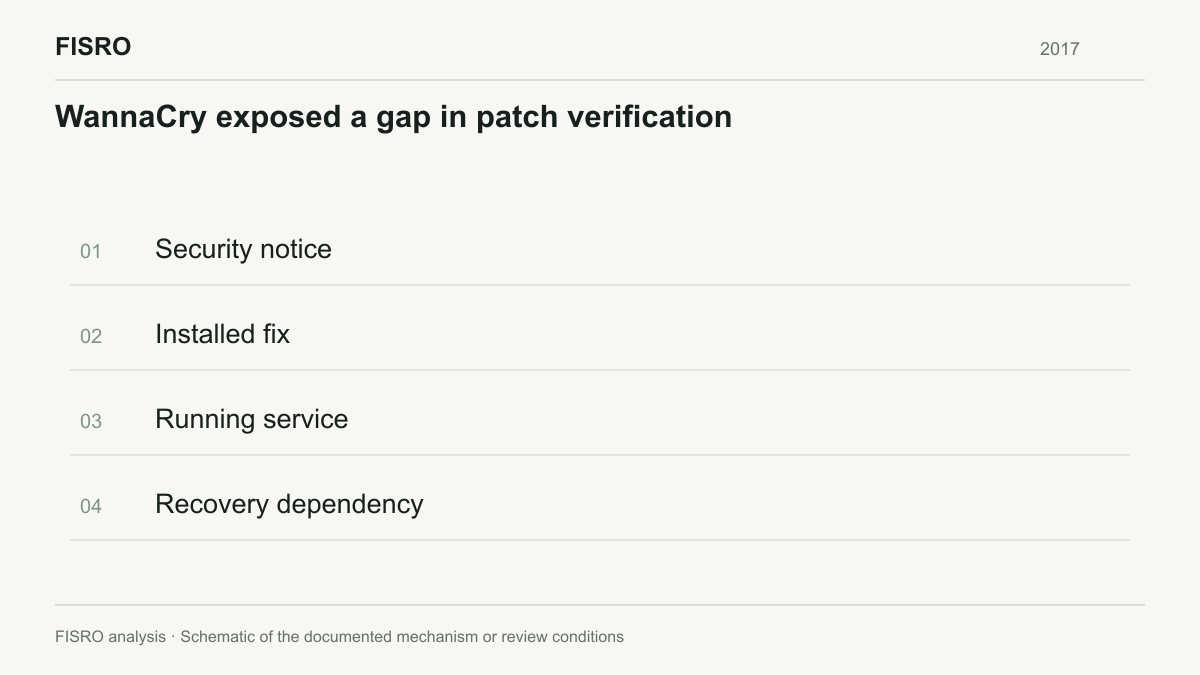
WannaCry, MS17-010 and the gap between a patch notice, installed software and a service that can recover.